Coast Guard says insider threat alert led crew to stop armed member
The US Coast Guard says intelligence from its insider threat programme enabled a cutter crew to stop an armed colleague boarding in March 2024.
 By Priya RamanTechnology Correspondent3 min read
What happened
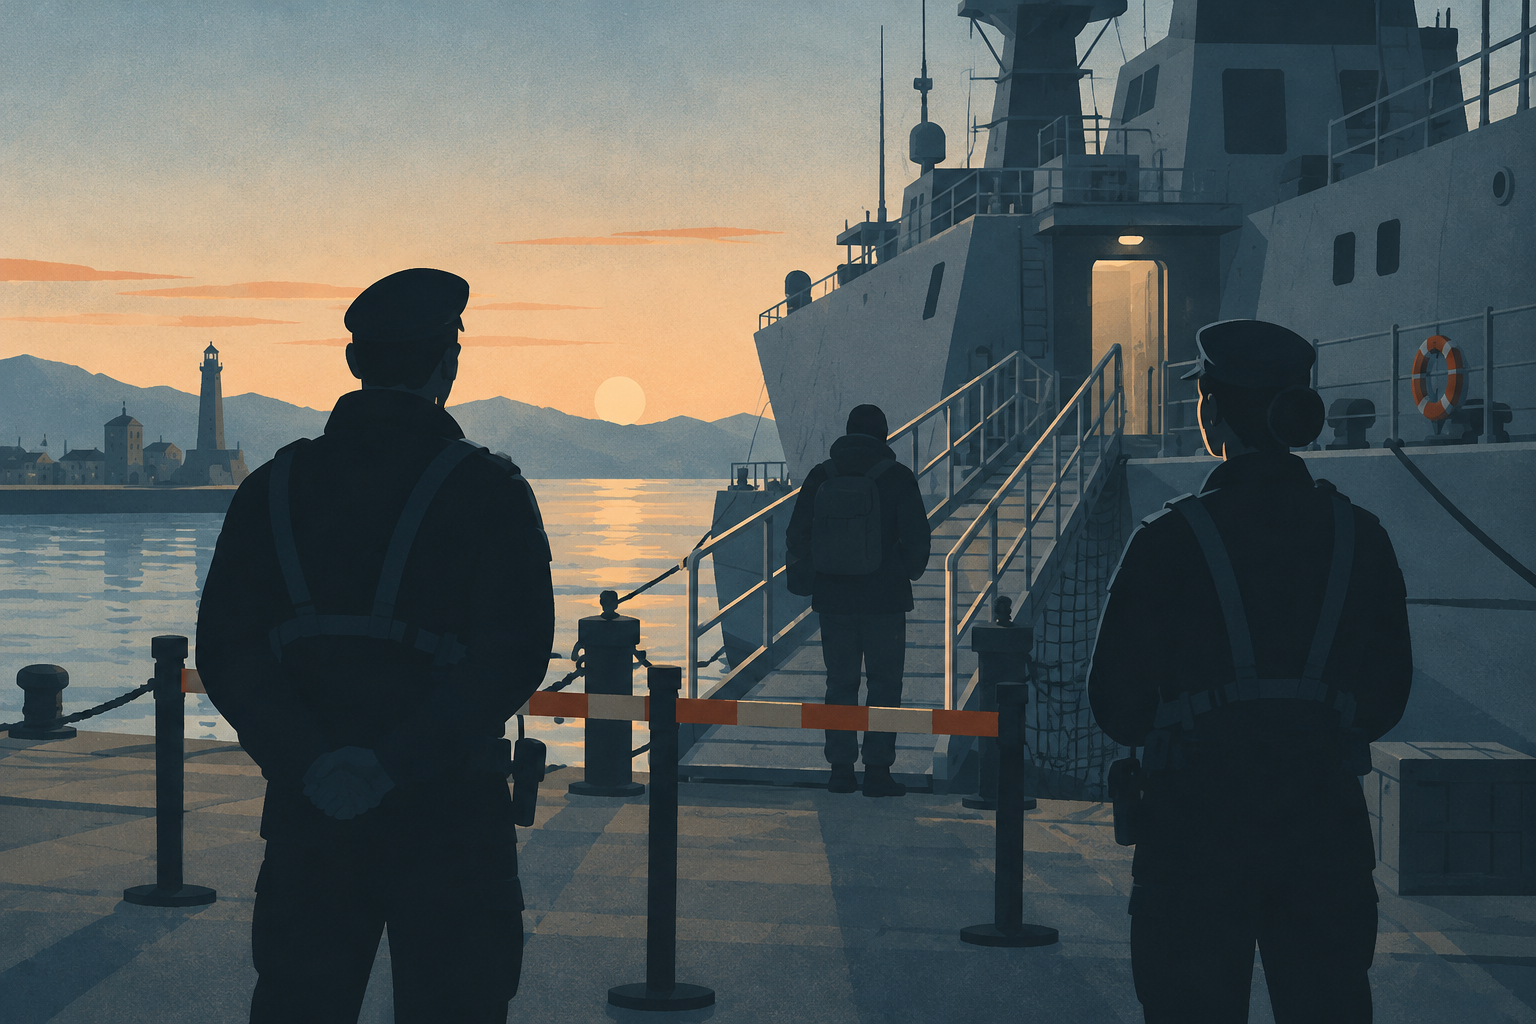
A US Coast Guard cutter crew stopped a service member boarding with a firearm and several ammunition magazines in March 2024 after an alert from its insider threat programme, according to the service.
The account, published by the Coast Guard’s MyCG news service, said the Coast Guard Insider Threat Program (CGITP) gathered intelligence and warned the unit so the individual could be apprehended. The crew confiscated the weapon and ammunition.
The service member has since been discharged, MyCG reported. The article does not identify him, name the vessel or give its location. It also does not describe his intentions or report any criminal charges.
The Coast Guard highlighted the intervention in an article marking National Insider Threat Awareness Month in September 2025. Its account does not explain how the intelligence was obtained or establish whether a colleague’s report prompted the warning.
The background
The Coast Guard established CGITP in 2015 to identify and address threats before they cause harm. The programme has 23 staff and is managed by Jared Quance, according to MyCG.
The service defines an insider threat as someone who uses access to its personnel, premises, systems or information in a way that causes harm, whether deliberately or unintentionally. Its examples include disclosure of sensitive information, equipment sabotage, harassment and violence.
That definition extends beyond cybersecurity. It treats the safety of people and physical assets as part of the same remit as protecting information, rather than limiting insider threats to stolen files or misused computer accounts.
The programme trains personnel to recognise concerning behaviour and gives supervisors and colleagues ways to intervene early. MyCG also identifies the Department of Homeland Security, the Cybersecurity and Infrastructure Security Agency and the Secret Service as partners.
The emphasis on training and collaboration is also reflected in private-sector guidance. As previously reported by Insider Threat Roundup, Adaptive Security recommends combining staff training, technical monitoring and shared oversight to address deliberate misuse, mistakes and compromised accounts. The Coast Guard account adds a physical-safety example to that broader discussion.
What people are saying
“We don’t get a lot of ground-level reporting from the field,” Quance told MyCG. He said he wanted personnel to submit more reports.
Quance encouraged staff to notice changes in colleagues’ behaviour, including signs of distress, aggressive language or unusual treatment of sensitive information. He also urged personnel to support colleagues, saying apparent security concerns can sometimes reflect a need for help.
MyCG cited the 2009 Fort Hood shooting, in which 13 people died, as an example of the potential human cost of internal threats. It separately highlighted the toll of military suicides on service members and their families.
The publisher said the 2025 awareness campaign focused on collaboration across the service, sharing information and prioritising staff well-being. Its guidance presented early reporting and support for colleagues as complementary responsibilities.
What happens next
Personnel can raise concerns through their command, a security officer or directly with CGITP, according to the guidance. Reports can be anonymous, providing an option for people who do not want to identify themselves.
MyCG directs staff to the programme’s SharePoint site for further information and to national awareness-month resources and events. The article does not set out a new policy, an expansion of the programme or a timetable for further changes.
No further proceedings involving the discharged service member are described. The published account therefore establishes an intervention and a subsequent discharge, but not a criminal finding or a planned attack.
Timeline
2015
The Coast Guard established its insider threat programme to identify and address internal threats.
March 2024
A cutter crew stopped an armed service member boarding after receiving intelligence from the programme.
September 2025
The awareness-month campaign emphasised collaboration, information sharing and staff well-being.
Why this matters
The Coast Guard account shows how insider-risk work can connect intelligence gathering with action to protect personnel, not only information systems. For organisations, the relevant lesson is the importance of clear routes for raising concerns and passing information to those able to respond. The guidance also places employee support alongside security intervention. Its limited detail warrants caution: the reported outcome does not establish the individual’s intentions or show which information first brought him to the programme’s attention.
Questions and answers
- what happened when an armed Coast Guard member boarded a cutter?
- In March 2024, the on-duty crew stopped a service member boarding with a firearm and several ammunition magazines. The Coast Guard said its insider threat programme had alerted the unit using intelligence it had gathered.
- was the armed Coast Guard member charged?
- The Coast Guard’s MyCG article says the service member was discharged. It does not report criminal charges, identify him or describe his intentions.
- what is the Coast Guard insider threat programme?
- The Coast Guard established the programme in 2015 to identify and address internal threats. Its work includes staff training, support for early intervention and cooperation with other agencies.
- how does the Coast Guard define an insider threat?
- The Coast Guard describes an insider threat as someone whose access to its people, premises, systems or information causes harm through deliberate or unintentional misuse. Examples include sensitive information leaks, sabotage, harassment and violence.
- how can Coast Guard personnel report an insider threat?
- Personnel can contact their command, a security officer or the Coast Guard Insider Threat Program directly. The service’s guidance says reports can be anonymous.
- what warning signs does the Coast Guard ask staff to report?
- The guidance asks personnel to notice behavioural changes, signs of distress, aggressive language and unusual handling of sensitive information. It also urges support for colleagues who may need help.
- when is National Insider Threat Awareness Month?
- National Insider Threat Awareness Month takes place in September. The Coast Guard’s account says the 2025 campaign emphasised collaboration, information sharing and staff well-being.
Sources
This report is based on original reporting and publications from:
Insider Risk Management
CISA issues guidance on building insider threat management teams
The US cybersecurity agency recommends bringing security, human resources, legal and operational expertise together, with safeguards for sensitive employee information.
29 October 2026
Insider Risk Management
Insider risk survey finds low confidence in early detection
Only 23% of surveyed cybersecurity professionals expressed strong confidence in detecting insider threats before serious damage, according to research by Cybersecurity Insiders and Cogility.
29 October 2026
Insider Risk Management
Proofpoint warns AI will widen insider threat risks in 2026
The cybersecurity company predicts AI agents and employee use of assistants will create new data risks, while also helping security teams investigate potential incidents.
29 October 2026
Insider Risk Management
SentinelOne puts annual insider threat costs at $19.5m
The cybersecurity company's 2026 overview highlights employee mistakes, stolen accounts and unauthorised AI use, but leaves important differences between its statistics unexplained.
29 October 2026